DreaMarz helps organizations protect what matters and make smarter decisions with their data. Our work brings security and analytics together under one roof — from threat monitoring and IT audit to enterprise dashboards and data insight.
Strong protection depends on understanding your data, and good data decisions depend on systems you can trust. By uniting both disciplines under one team, DreaMarz eliminates costly vendor hand-offs and structural blind spots.
Hands-on defense, risk mitigation, and compliance readiness designed for high-growth tech stacks. We don't just point out vulnerabilities — we configure controls and investigate incidents.
Transform scattered business and telemetry data into trustworthy pipelines, executive dashboards, and dependable operational models that drive decisive leadership.
Five specialized practices, delivered by senior practitioners with deep backgrounds in both security operations and data engineering.
Continuous telemetry ingestion, SIEM fine-tuning, alert noise reduction, and behavioral anomaly detection across multi-cloud environments.
End-to-end audit readiness for SOC 2 Type I/II, ISO 27001, and HIPAA. We implement actual technical controls, not just bureaucratic checklists.
Rapid incident response, compromise assessments, and forensic log reconstruction to identify threat vectors, isolate breaches, and restore operations.
Transform convoluted databases and metrics into intuitive, automated executive dashboards with real-time alerting and predictive KPIs.
Robust data engineering: ETL/ELT pipelines, schema normalization, automated cleansing routines, and dependable operational reporting loops.
Run through our 2-minute interactive assessment to evaluate your security controls and data maturity. Get an instant score and custom recommendations.
Discover hidden compliance liabilities, data pipeline bottlenecks, and monitoring blind spots before they impact your growth or audit milestones.
Average posture uplift achieved by DreaMarz clients within 90 days.
How combining hands-on security engineering with advanced data architecture solves mission-critical business challenges.
A Series-A fintech required immediate SOC 2 Type II compliance to unlock Tier-1 enterprise sales pipelines, but lacked automated audit evidence trails.
Engineered automated AWS IAM evidence pipelines and unified audit logs directly into compliance dashboards, closing 14 enterprise deals.
Growing patient telemetry required complex clinical analytics while guaranteeing zero unauthorized PII/PHI exposure across distributed provider teams.
Deployed granular column-level encryption, automated PII cleansing, and real-time clinical KPI dashboards for senior medical directors.
Scattered bot attacks and payment anomalies were overwhelming support and security engineers without actionable cross-system correlation.
Consolidated payment gateway logs and CDN threat events into a single real-time anomaly detection pipeline with instant Slack/PagerDuty triage.
Founded by a team that combines cybersecurity expertise with deep data and engineering backgrounds, DreaMarz helps businesses stay secure and informed as they grow.
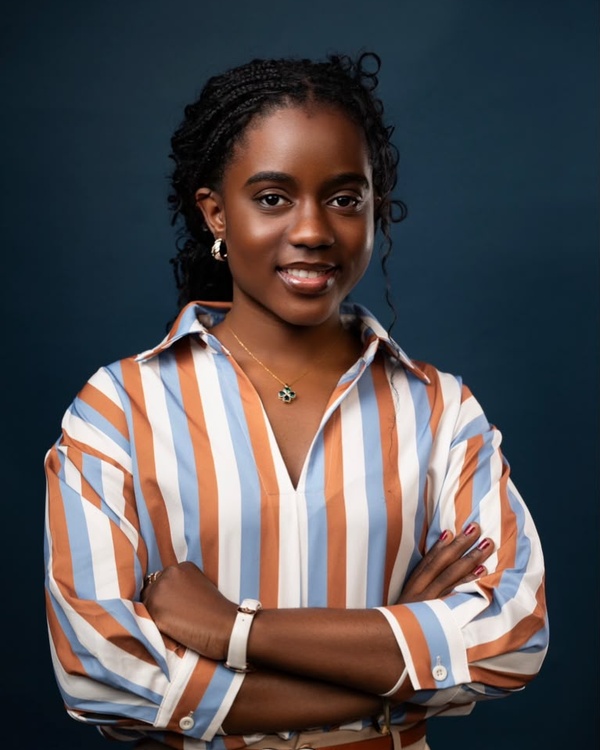
Joanna leads the Cybersecurity, Governance, Risk & Compliance (GRC), and Digital Forensics practice at DreaMarz. With hands-on expertise across enterprise security architecture, IT audit frameworks (SOC 2, ISO 27001, NIST, HIPAA), and proactive threat hunting, she ensures client systems remain fortified and audit-ready against complex threat landscapes.
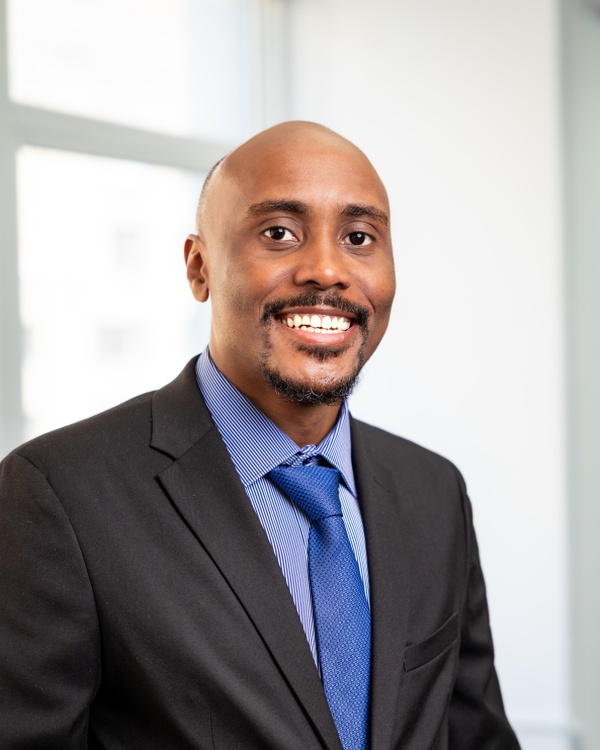
Emmanuel leads the Data Intelligence, Engineering Pipelines, and Analytics practice at DreaMarz. Combining deep technical engineering with business intelligence strategy, he specializes in architecting high-throughput data pipelines, automated data cleansing, and executive visualization dashboards that convert unstructured data into clear, high-conviction decision engines.
Everything you need to know about partnering with DreaMarz for cybersecurity and data intelligence.
Security and data are fundamentally two sides of the same problem. Effective cybersecurity relies entirely on understanding your data assets, access patterns, and log telemetry. Simultaneously, your data strategy is only as viable as the security and integrity of the systems hosting it. Having one partner manage both eliminates the typical friction and finger-pointing between security teams and data engineers.
Yes. Many clients start with an immediate need — such as an upcoming SOC 2 Type II audit, a threat investigation, or building an executive PowerBI/Tableau pipeline. As your needs evolve, you can tap into our broader dual-discipline capabilities without onboarding a new vendor.
We operate under a strict Mutual Non-Disclosure Agreement (MNDA) before reviewing any client architecture. All telemetry access is configured following the principle of least privilege (PoLP) and zero-trust guidelines, using dedicated, encrypted client enclaves with zero shared infrastructure.
We specialize in serving high-growth startups, mid-market organizations, and tech-forward enterprises that require institutional-grade security and data capability without the overhead of massive, sluggish management consulting firms.
Engagements typically start with a 30-minute discovery consultation or an initial Security & Data Maturity Diagnostic. We review your current architecture, identify immediate compliance or visibility risks, and deliver a clear, fixed-scope proposal.